Physical security: What it is, why it fails, and how to build it right
Get your free physical security guide
Four pillars, eleven trends, and the checklist your next audit needs.


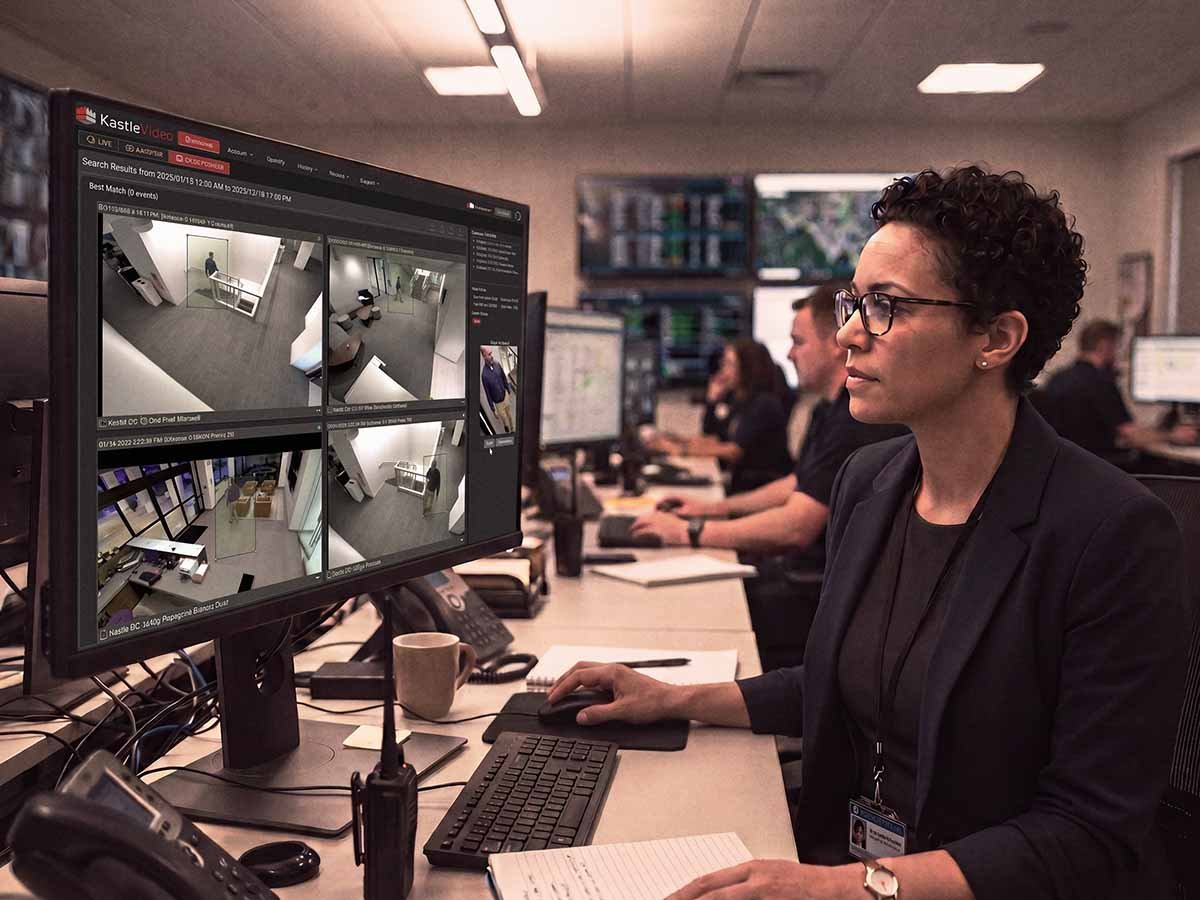
Most buildings have a keycard reader, a security camera in the lobby, and a guard at the desk for security. What you won’t always find is a security program. That difference between the two only comes to light after something goes wrong. By then, the property and corporate security teams are already paying heavily for the lapse.
On their own, those components are just hardware. Without deliberate design and management, they cannot replace a security program. The latter is a system built on active oversight, clear accountability, and defined incident response. The distinction here may seem minor, but the operational gap it creates is much larger.
Undetected intrusions, unauthorized access, and similar physical security threats rarely happen because the alarm systems didn’t trigger. They happen because no one is actively managing them. This is why property teams and building owners need a thorough framework and can’t rely solely on a feature list. They need to understand where their physical security risks lie before buying whatever equipment a vendor recommends. A real framework and a clear view of risk both start with knowing what strong security solutions actually look like.
The physical security that actually matters
The physical security definition most property teams work with is too narrow. They focus on cameras and door locks. IT teams focus on server rooms and data centers. Building managers focus on entry points. All these are part of it, but they don’t fully define end-to-end physical security measures.
Physical security is a layered approach to protecting physical assets, property, information, and people from threats such as theft, vandalism, unauthorized access, and physical harm. It includes access control, visitor management, video surveillance, intrusion detection, emergency response, and ongoing monitoring, all coordinated under a single management framework.
The importance of physical security extends beyond just detecting incidents after they happen. It also lies in deterring threats before they escalate, detecting suspicious activity in real time, delaying unauthorized access long enough to trigger a response, and defending against threats after they are identified. The security industry calls this the “4 Ds” framework, which stands for Deter, Detect, Delay, and Defend. Strong physical security relies on all these different layers working together. Even if one is underperforming or missing, the whole system struggles to function as it should.
Why physical security systems fail: the gaps that matter
A 2025 Pro-Vigil survey found that 88% of respondents reported physical security incidents stayed the same or increased. The physical security market now exceeds $129 billion and is growing at a 7% CAGR, driven largely by rising threats. Property teams invest heavily in security systems, but spending isn’t the problem. Most failures aren’t technology failures. The security cameras function as intended. The motion sensors trigger alerts when something goes wrong. The gaps here are operational and structural.
Physical security system failures at a glance
-
No ongoing management after installation.
-
Detection systems with no defined response process.
-
Fragmented vendors with no shared visibility.
The lack of ongoing management
Physical security solutions help security teams respond promptly, but that response isn’t possible when systems are installed and left unmanaged.
A security camera is equipped with smart sensors to provide complete situational awareness. The vendor walks through the features, hands over the credentials, and moves on. The installation is done from their perspective. But from the building’s perspective, the real work is just starting, and often no one is formally assigned to do it.
Access permissions accumulate without proper reviews. Former employees still possess active credentials because there was no security offboarding. Cameras lose connectivity without sending notifications. Monitoring responsibilities fall to whoever happens to be nearby.
This is the result of nobody actually owning security measures, which are treated as a setup task rather than an ongoing function. Systems age, and people leave. Without active management, the system is bound to become less reliable over time.
Physical security technology without a response is not protection
From video management systems to occupancy sensors and AI security cameras, there are different types of physical security solutions that buildings can employ. But those are all for detection. Many teams fail to realize that response is equally important and conflate detection with protection.
Detection creates records. For example, an unrecognized individual may tailgate behind an employee carrying their ID card. Response determines the outcome here. It decides whether that individual is caught or slips past security.
A motion alert triggers notifications to a dashboard that no one monitors overnight. A camera records unauthorized access events, but no one is reviewing the footage. An alarm triggers at 3:00 AM, and its notification remains in the inbox until 8:00 AM. All of these are detections without a response. None of those systems failed, but the outcome was the same as if a security failure had occurred.
The difference between detection and a full security program becomes clearer when mapped to real scenarios.
| Scenario | Detection only | Detection + response (a program) |
|---|---|---|
| 3:00 AM intrusion alert | Recorded and queued, but reviewed hours later | Monitored in real time and acted on immediately |
| Credential belonging to a former employee | Remains active until someone flags it manually | Revoked through a managed offboarding process |
| Blind spots across multiple vendors | Systems operate independently, and events are correlated manually | Unified under a single platform with shared visibility |
-
3:00 AM intrusion alert
Detection only
Recorded and queued, but reviewed hours later
Detection + response (a program)
Monitored in real time and acted on immediately
-
Credential belonging to a former employee
Detection only
Remains active until someone flags it manually
Detection + response (a program)
Revoked through a managed offboarding process
-
Blind spots across multiple vendors
Detection only
Systems operate independently, and events are correlated manually
Detection + response (a program)
Unified under a single platform with shared visibility
Physical security programs that focus solely on recording and logging, without implementing ongoing monitoring, are structurally incomplete. They leave gaps that are nearly invisible until an incident makes them obvious.
Fragmented systems create inevitable blind spots
The third, and one of the most common, failure patterns is system fragmentation. Access control comes from one vendor, surveillance from a second, visitor management from a third, and security personnel from a fourth. Each vendor has their own systems, dashboards, maintenance requirements, and support lines.
The result is that no one has sufficient visibility into what’s happening across the building at any given time. An unauthorized access incident at the rear entry point doesn’t automatically correlate with the surveillance system over it. A person flagged by the visitor management system still enters the building because access controls weren’t updated in real time. And these gaps exist because the security systems aren’t communicating with one another.
Fragmentation is a structural vulnerability that ultimately leads to severe physical security risks. The more isolated each system is, the more it depends on someone manually piecing events together. Building personnel, who are already busy managing tenants and daily operations, aren’t always available to do that.
This is why fragmentation is the most difficult failure pattern to fix with more technology. When no single party is responsible for how they work together, each vendor owns their piece, but nobody owns the outcome. Property teams end up as the unofficial integrators, manually stitching systems together between service calls and hoping nothing slips through. The model itself is the vulnerability.
The pillars of physical security
Implementing the right physical security techniques requires a clear understanding of what each component is designed to do. They serve specific functions, and when they work together under unified management, building security rests on both detection and response.
Access control at a glance
-
Governs who can enter which areas, at what times, and under what conditions.
-
Includes keycard readers, key fobs, and coded access control readers.
-
Supports role-based permissions and mobile credentials.
-
Offers time-based restrictions and cloud-based administration.
Access control is at the heart of physical security. It governs who is permitted to enter which areas, at what times, and under what conditions. A well-designed access control system establishes a verifiable movement pattern throughout the building that can be reviewed and audited as needed.
Modern access control goes far beyond keycard readers and key fobs. It also includes access control readers that verify users with assigned codes, role-based permissions managed on centralized platforms, and mobile credentials that let users carry access on their phones.
Some systems also provide time-based access control to automatically restrict entry outside business hours. Cloud-based management helps stakeholders manage these controls and access credentials remotely. This is particularly useful for security teams handling properties across multiple locations.
That said, access control alone cannot verify that the right individual is using a credential. A stolen keycard will still grant entry. That’s why access control systems work best as part of an integrated security program, especially when paired with video surveillance to visually confirm who’s accessing entry points.
Video surveillance at a glance
-
Verifies who is actually entering through an access point.
-
Uses AI-driven video analytics for real-time monitoring.
-
Detects suspicious behavior in real-time, not after the fact.
-
Runs on cloud-based video management for remote access to footage.
Access control determines who can enter, while video surveillance verifies that the right person actually did. Stolen credentials or tailgating events won’t trigger access control alerts because the entry is still legitimate to the system. Real-time video surveillance is the layer that detects what access control might overlook.
A camera that captures footage for post-incident review is an investigation tool. Modern surveillance systems pair high-resolution cameras with AI-driven video analytics for real-time monitoring. These systems detect suspicious behavior in real time and deliver alerts to monitoring personnel as the situation unfolds. Security moves from just reviewing incidents after they happen to responding to them before they can escalate.
Cloud-based video management removes the burden of installing on-premises infrastructure. Video footage is immediately accessible from authorized devices, and security personnel can verify alerts against it within seconds.
Visitor management at a glance
-
Manages contractors, vendors, clients, and guests who lack permanent credentials.
-
Runs pre-registration workflows to authorize expected visitors.
-
Verifies visitor identity at check-in.
-
Applies time-limited access once a visitor is inside the building.
Access control manages a defined group of employees, residents, and authorized personnel with assigned credentials. But in any commercial building, a significant portion of daily traffic falls outside that group. Contractors, vendors, clients, and guests don’t carry permanent credentials, and their access requirements may not be set until they arrive.
Building security remains vulnerable to threats when that gap exists. Employees who no longer have access or contractors flagged for security concerns can still enter if the visitor management system isn’t communicating with access control. This is why visitor management is central to addressing the fragmentation problem. Management systems that operate independently may add processes but not security. They may capture check-in data, but that never reaches access control, and re-entry can’t be prevented.
Visitor management delivers real value when integrated into the broader security program. Management systems run pre-registration workflows to authorize expected visitors for temporary access. ID verification happens during check-in. Hosts receive alerts confirming the visit is expected, and time-limited access governs where the visitor can go once inside.
Threat deterrence at a glance
-
Uses perimeter fences, secured entry points, and physical barriers.
-
Applies visible signage indicating active on-site security.
-
Relies on visible cameras and adequate lighting throughout the building.
-
Reduces the burden placed on detection and response systems.
Deterrence is the first “D” of the 4 Ds framework. Yet most buildings overinvest in detection and neglect deterrence, which is the opposite of what should happen.
A deterrence-first posture has a simple logic. Security programs don’t have to detect, delay, or respond to threats that don’t materialize. Environmental measures such as perimeter fences, secured entry points, and physical barriers form the first line of defense against unauthorized access. Clear signage indicating active on-site security influences a would-be intruder’s decision-making before any physical security technology steps in. Visible cameras, adequate lighting throughout the building, and clearly marked entry points make trespassing difficult and, if it still occurs, more likely to be caught.
Security programs often focus heavily on detection infrastructure. They bring on as many cameras, sensors, and alarms as possible without giving much thought to environmental design that can reduce the likelihood of incidents. The consequence is a program geared toward response instead of prevention.
Effective deterrence is a core component of physical security best practices that support comprehensive protection. It matters most in buildings such as multifamily residential properties, where residents, guests, and vendors come and go around the clock. When combined with access control, visitor management, and video surveillance, deterrence completes the kind of building security that makes intruders reconsider before breaching a building. Risks still exist, but the burden on detection and response systems decreases significantly.
Recent trends in physical security solutions
The fundamentals of physical security haven’t changed, but the technology used to execute them is evolving rapidly. Rising business expectations and security complexity mean property teams must keep pace with current physical security trends to adopt the right protection.
Video surveillance is driving real-time response
One of the most subtle shifts in physical security is the reliance on video verification for response credibility. Security teams want real-time information on what’s happening before things can escalate. This is driving the need for video verification in security programs, using intelligent camera systems and AI-driven video search to detect movement before it becomes a threat.
AI-enabled platforms are replacing reactive security
AI and predictive analytics are the biggest developments at the system level. Security leaders are moving towards AI-enabled platforms because they can identify behavioral patterns before incidents occur. People and vehicles are detected from long distances, and any unusual access sequence, movement pattern, or suspicious event is flagged in real time.
Cloud-based security is becoming the default
Cloud-based security is restructuring how teams implement protection. Security leaders and Global Security Operations Centers (GSOCs) want the agility of centralized management, remote configuration updates, and real-time visibility into system health. This is also evident in the Video-Surveillance-as-a-Service (VSaaS) market. It is expected to exceed $14 billion by 2032, driven by the shift from on-site recording to cloud-based monitoring platforms.
Mobile credentials are the new keycards
Mobile credentials are quickly replacing commercial keycards. They place no burden on users, provide greater administrative flexibility for operators, and are more difficult to clone or transfer than physical keycards. Security moves from effort to convenience, and teams gain better control over who has access.
Physical-cyber convergence is no longer optional
Security leaders are increasingly focusing on unifying physical and cybersecurity infrastructure to create more comprehensive security programs. Those who treat the two separately are managing a risk surface as two different problems, leaving them exposed to blind spots in both areas. Centralized security dashboards, unified threat detection platforms, and cross-functional response strategies are becoming prominent because cybersecurity underpins every component of physical security ecosystems today.
How managed security solutions can close the gap
The conventional approach to building security programs has a structural problem. Teams source the best access-control platforms, security-camera vendors, and monitoring services. Maintenance is handled by the vendor, who picks up the phone. Each one is responsible for their system, but no one takes accountability for the overall security outcome.
That distinction is where security programs fail. When cameras lose connectivity, their vendor addresses the hardware. When an access control system flags a threat, the monitoring provider responds to what falls within their agreed contract. The accountability gap here isn’t dramatic, but it is a persistent issue that only becomes apparent when an incident exposes it.
The alternative is a one-partner physical security model. A single accountable partner that offers operational ownership and eliminates fragmentation from the security picture. When something needs attention, one call resolves it, with no gaps in protection and no vendor finger-pointing.
This is what a managed security model looks like in practice.
-
One partner owns every stage of the security lifecycle, including design, manufacturing, installation, monitoring, and maintenance.
-
There are no gaps in protection because only a single provider is accountable.
-
Under this model, security is an outcome, not an asset that a business has to run on its own.
Kastle has operated this model for more than 50 years, protecting over 10,000 properties and 60,000+ businesses across the United States and Australia. That single relationship covers design through ongoing maintenance. The full lifecycle sits with one provider rather than being spread across four or five.
Physical security is a holistic program. Its components are well understood but rarely executed with the expertise they demand. A surveillance system isn’t a security program. An access control system isn’t either. Even a combination of both, sourced from reliable vendors, isn’t a holistic security solution. That is something teams can achieve when they also bring in active monitoring, ongoing maintenance, actionable detection, and complete accountability.
Physical security, when done right, is layered by design, with every component working alongside the others to maintain protection. Access control, surveillance, visitor management, and deterrence reinforce one another. Every alert has an owner, and every gap has a process to manage it before it becomes a liability.
That level of security comes from unified management and an active response. It is the standard and achievable, but only when property teams treat physical security solutions as an end-to-end, ongoing effort. That’s how property teams get better tenant satisfaction, simpler site management, and reduced operational burden.
Frequently asked questions
Physical security is a layered approach to protecting people, property, assets, and information from threats such as theft, vandalism, unauthorized access, and physical harm. These security systems operate on deterrence, detection, delay, and defense, which work together to deliver end-to-end protection.
A security system refers to the hardware, such as surveillance devices, employee keycards, and motion detectors. A security program weaves security systems together with active oversight, clear accountability, and defined threat responses. One facilitates threat detection, while the other ensures threats are detected and responded to before they escalate.
The difference here lies in who owns the security infrastructure, who manages it, and who should be held accountable. On-premises physical security means the building owns and manages security in-house. Hardware lives on-site, software runs on local servers, and all responsibility falls to the in-house staff.
Managed physical security transfers the responsibility to a dedicated provider. They manage the entire security lifecycle, from designing the system to installing the security program and maintaining it over time, as Kastle has done for 50+ years.
Ask the provider:
- Who is responsible for the security system after installation
- Who to call when a software update stalls
- Whether monitoring is outsourced
- Whether platform integrations are available
- What happens to the system as your business scales
A fully managed security solution consolidates multi-site security under a single program. Property teams have access to an integrated program with a single point of contact for designing, installing, monitoring, and maintaining security.
That’s precisely what Kastle provides. It offers a consolidated security solution with cloud-based access control, integrated data reporting for all locations, centralized monitoring, regular remote software updates, and a dedicated team for ongoing services.
This depends on how the security program was designed. If it’s only cloud-based without any local backup, the connected security systems may not work as intended. However, most cloud-based security solutions are designed to keep functioning during outages. With a fully managed service provider, teams can also coordinate with their point of contact to quickly find a solution, rather than chasing vendors during outages.
Physical security refers to protecting people, property, and assets from physical threats, like unauthorized access and vandalism. This primarily involves using systems like access control, video surveillance, and security signage. Cybersecurity, however, refers to protecting networks, data, user credentials, and similar digital assets from digital theft and disruption. Endpoint protection, firewalls, and data encryption are some of its primary protocols.
The costs of a physical security system depend on the following factors:
- The size of the property
- Whether multiple locations or buildings are to be managed
- The scope of video surveillance required
- The number of access points
- Whether additional security solutions are needed, like parking management
That said, costs can be significantly higher when choosing individual vendors for different security systems than when using a single partner that fully manages the entire security lifecycle.
Tell us about your project and our team will follow up.